Sandfish vs other phishing tools: features, prices, and real cases
Compare Sandfish with urlscan.io, ANY.RUN, VirusTotal, Cloudflare Radar, Hybrid Analysis, and Joe Sandbox. See feature and price tables, plus what Sandfish adds in real cases.
Read article
How eight Magalu lookalike storefronts share one backend
A hostname lookup and a cart request connect eight lookalike stores. Following their configurations shows a shared backend and explains why an image match is not enough.
Read article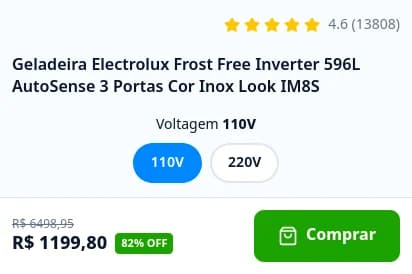
A broken agreement reference connects copied debt-relief pages
Two empty fields reveal how a fake debt-relief page makes its agreement reference. Exact code matches and a fixed-text copy show how the defect survives reuse.
Read article
What our pre-election phishing counts measure
Confirmed cases rose from two to 47 across two weeks. Changes in sources and review selection explain what the increase says about phishing before Brazil's runoff.
Read article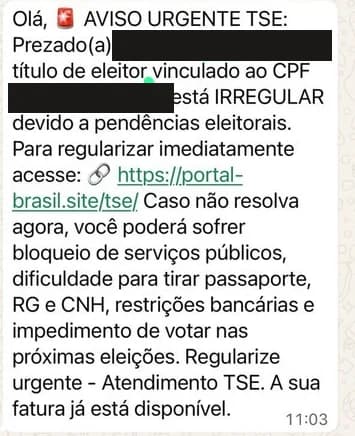
Weathered Raven: the contracts behind fake USDT transfers
A fake 1-USDT transfer form requested unlimited spending permission. Contract history links three actor clusters and explains a later 7,999.99-USDT transfer.
Read article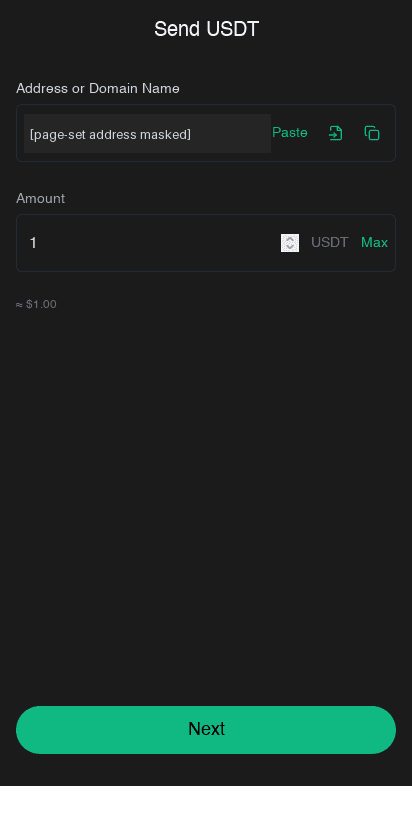
The OneDrive lure that sends a server-issued code to Microsoft's real sign-in page
A separate panel supplies a device code to a fake OneDrive document page. Six captures connect its verification interface, while server responses and client handlers expose configurable sign-in modes and failure handling.
Read article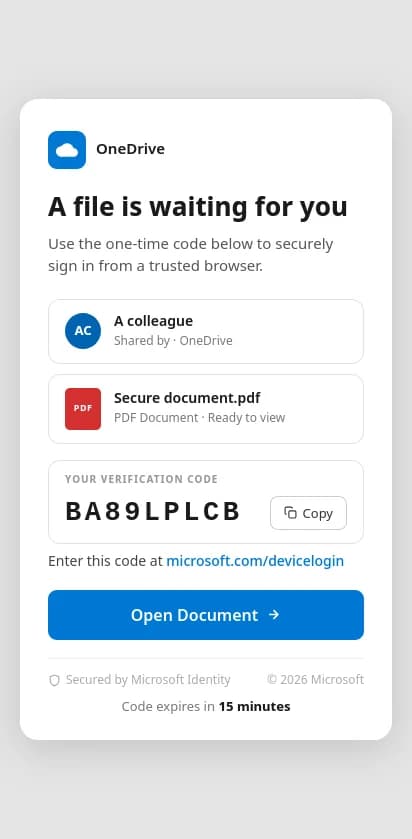
The DHL Track button that takes a camera frame and a GPS position
A fake DHL tracking page asks for the front camera and the precise location, then sends one frame, the coordinates, and the tracking number to its server. Two days earlier, a captcha that no visitor could solve blocked the same upload.
Read article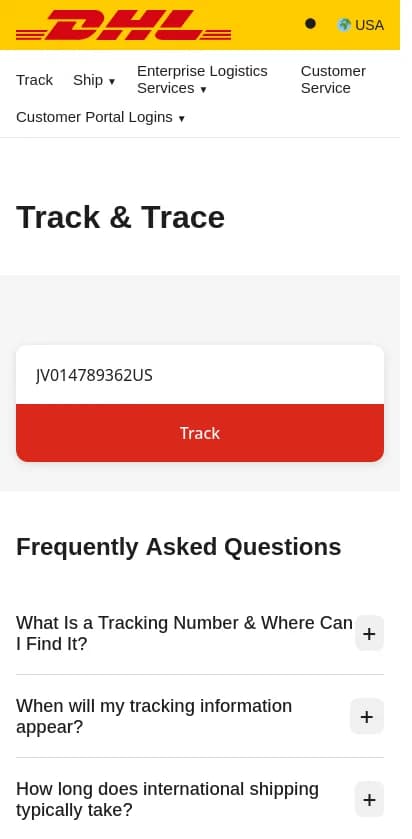
The SEUR address correction that ends with a card PIN
A €0.27 delivery-fee lure collects personal details, card data, an SMS code, and a card PIN. Shared files connect four reachable deployments; synthetic submissions lead to a claim of successful verification.
Read article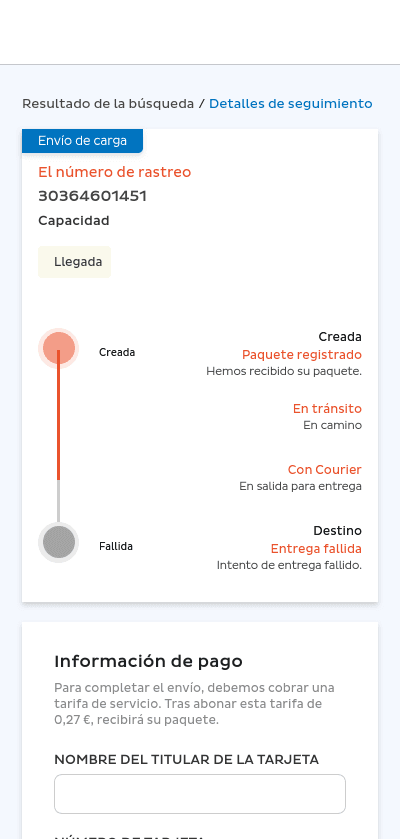
The R18.22 delivery fee that sends card details to Telegram
Sandfish follows a fake Courier Guy payment through card and SMS-code collection. Archived responses confirm delivery to Telegram; a related deployment reveals the difference between active collectors and copied settings.
Read article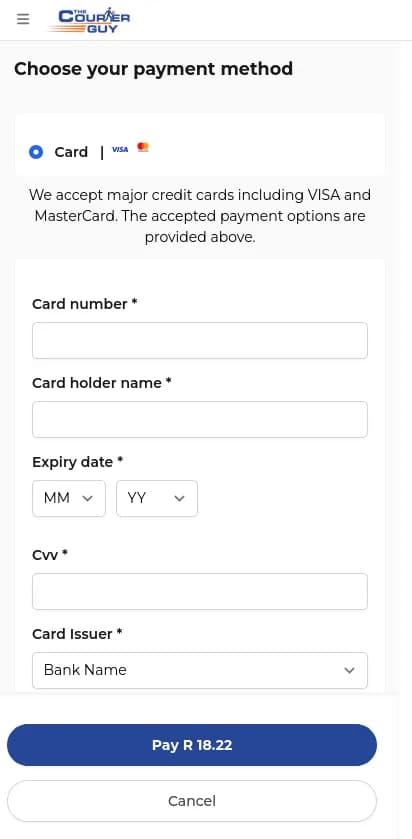
A fake Gencat login leaks the password twice
A copied Madrid login sends credentials to Formspark, then exposes them in an Outlook URL. An incomplete MFA option reveals how the imitation was assembled.
Read article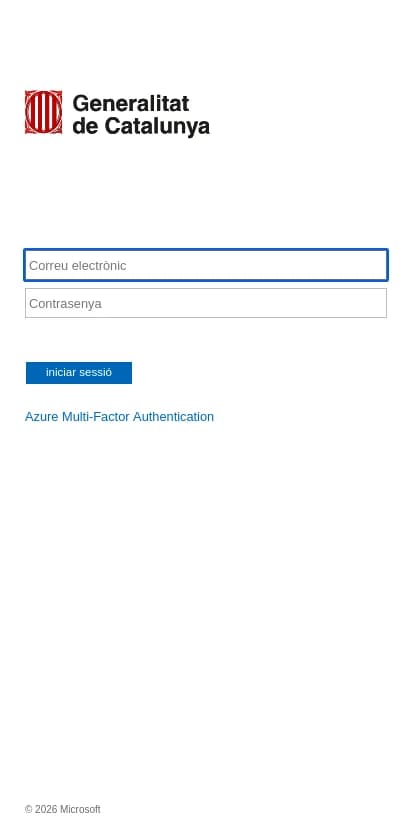
The checkbox that hides a phishing kit
An imitation Cloudflare check hides a configurable payment-phishing application. Its client code reveals commands for steering verification prompts; 2,076 public scans show the limits of gate-only captures.
Read article
Same bot, new domain: a US banking phishing campaign
Identical archives preserve a Telegram collection destination across changing domains. Inside, repeated login prompts and a brittle anti-bot dependency reveal how the banking kits operate.
Read article